Skills CLI
Installs, updates and removes agent skills for Claude Code, Codex, Cursor and more
by Vercel Labs
by BlockHacks.ioPluginWrite code
Checks whether an npm package has known security problems before you install it
Your AI assistant wants to add a package you have never heard of, and you have no quick way to tell whether it is risky.
For DevelopersTeams reviewing dependency changes
NPMScan is a plugin that connects Claude Code to npmscan.com's free, read-only package lookup service. Name a package, paste a package.json or lockfile, or give a GitHub repository link, and it reports known vulnerabilities, malware findings, maintainer changes and risky install scripts, with links to the full write-up. It also compares candidate packages and ranks what to fix first. It suits developers and teams reviewing the packages their projects depend on.
It needs no account or API key, and it reports a package flagged as malware as something to remove, not as an ordinary bug.
Start with the first one: it is a small task you can check easily.
Example prompts written by Agent Flows Hub.
From the creator's documentation.
| Output | What it is | Reads |
|---|---|---|
| Package lookup | Latest version, maintainers, license, downloads and install scripts for one package | Public npm data |
| Vulnerability check | Known vulnerabilities from OSV.dev, with malware findings marked separately | Public advisory data |
| Package check | Maintainer changes, publish provenance and an install-script scan for one package | Public npm data |
| Dependency audit | One report for a pasted package.json, lockfile or GitHub repository link | Your file, sent to npmscan |
| Package comparison | A side-by-side of 2 to 5 candidate packages with a suggested pick | Public npm data |
| Fix order | Findings ranked by what to fix first, with incident-response steps | What you paste |
Before you or your agent add a package, ask whether it has known problems. The plugin looks up public advisory and registry data through npmscan.com and returns one report per package or per dependency list.
Notes by Agent Flows Hub (original project name: npmscan-mcp-plugin), written from the creator's documentation, not from running it ourselves. NPMScan plugin for Claude Code: README · NPMScan MCP setup for other clients
Tell us what happened. We take a look first; if it needs paid work, you get an estimate before anything starts.
Installs, updates and removes agent skills for Claude Code, Codex, Cursor and more
by Vercel Labs
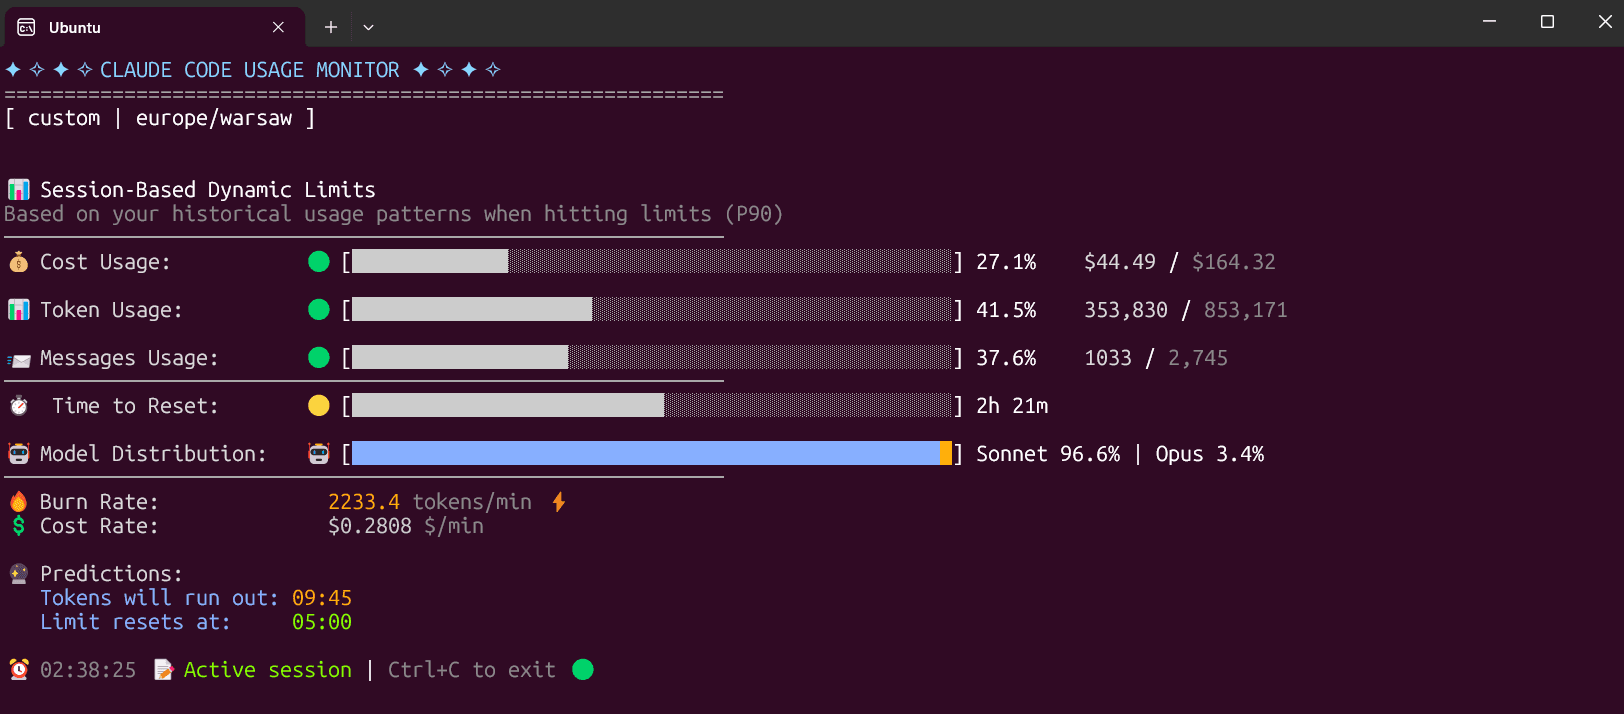
Shows your Claude Code usage live in the terminal and warns you before you hit a limit
by Maciej
Helps your coding agent draft a feature spec, then has fresh reviewers poke holes in it
by Google